Performance & maintenance
PHP2Shell & Node.js Critical RCE Updates: How to Patch Now
Critical RCE vulnerabilities hit PHP (PHP2Shell) and Node.js on October 21, 2026. Learn how CVE-2026-109618 and CVE-2026-111497 work, and how to properly rebuild your Docker containers to secure your Laravel and Node applications.
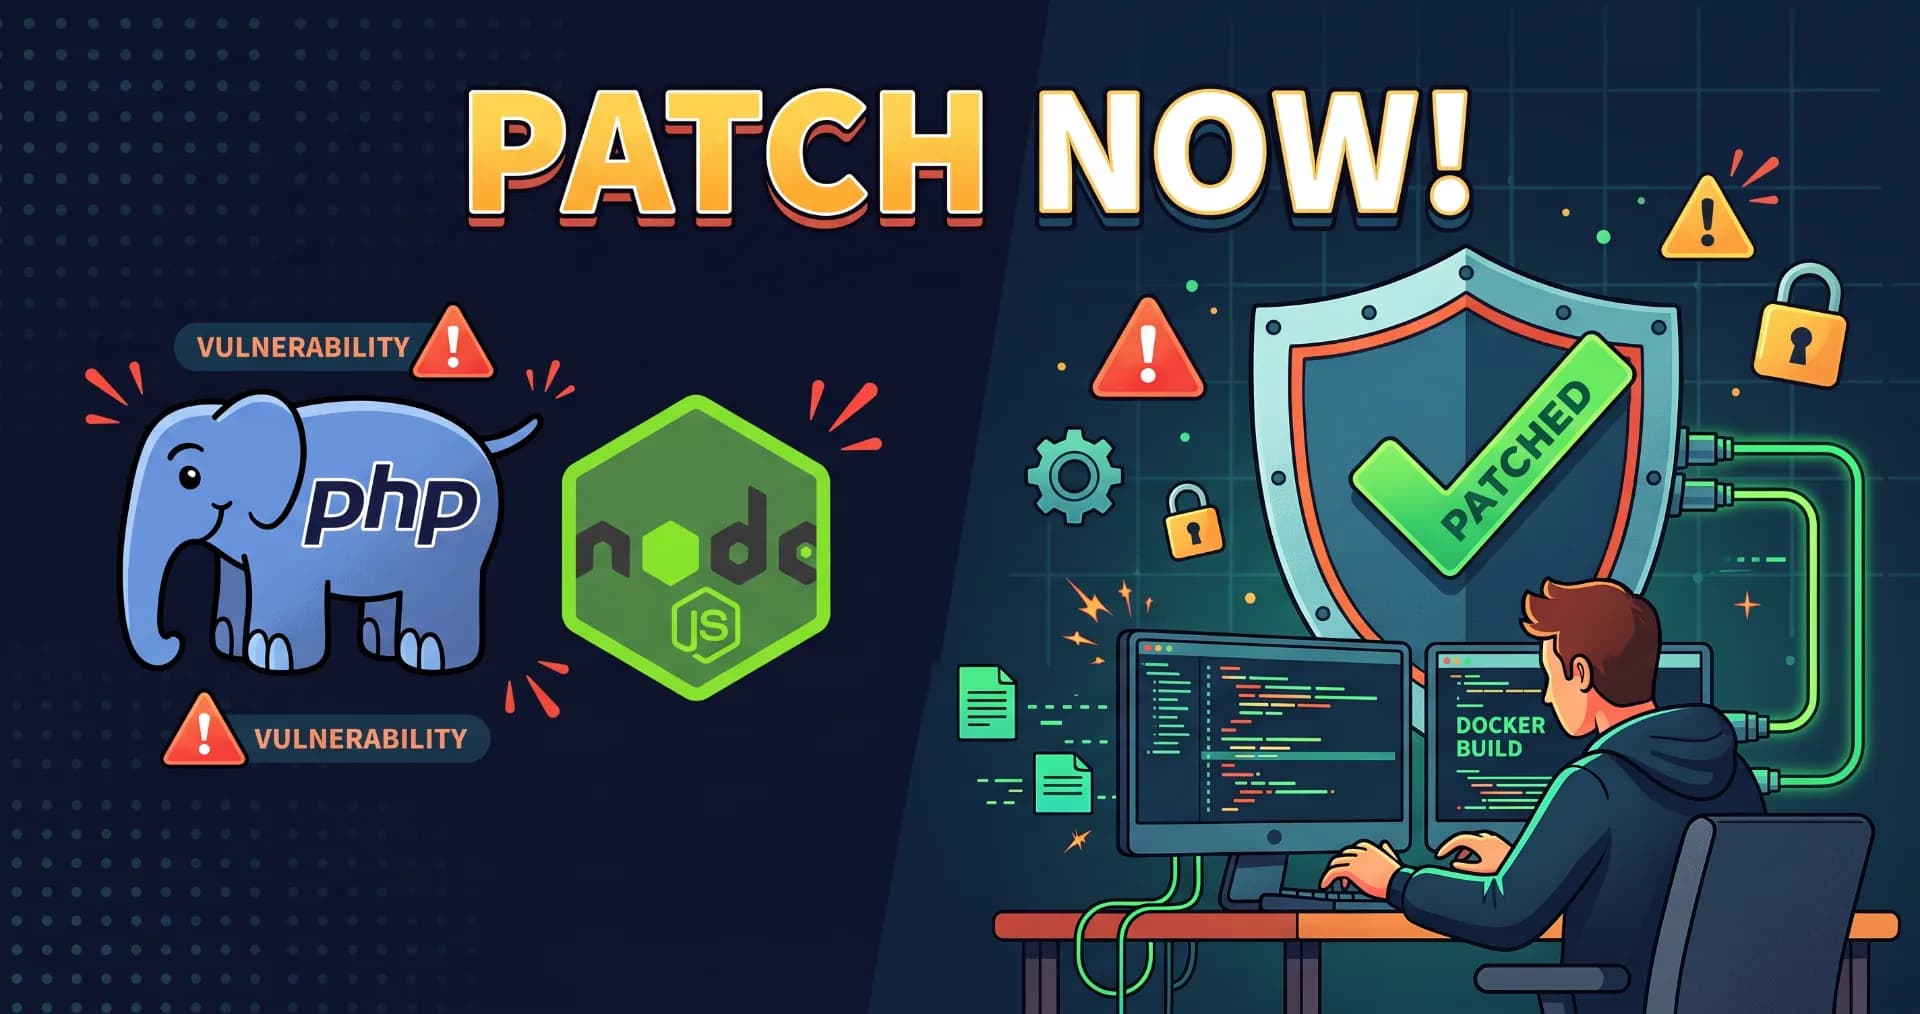
On October 21, 2026, the global web development ecosystem faced an urgent security crisis. Emergency updates were simultaneously dropped for both PHP and Node.js to patch highly critical, exploit-ready vulnerabilities.
This includes the high-profile "PHP2Shell" exploits allowing unauthenticated attackers to hijack web servers, alongside critical Remote Code Execution (RCE) bugs in Node's compression engine.
In-the-wild exploitation was detected by Amazon Threat Intelligence and other monitors days before the patches dropped. If you manage web apps, API backends, or microservices, you need to apply these updates immediately.
This guide cuts through the news noise to show you exactly how these vulnerabilities work, what is affected, and a foolproof, beginner-friendly step-by-step tutorial on how to apply the fix across Linux, Windows, macOS, Docker, and local environments.
🚨 Understanding the Threats (Why This is Urgent)
To understand how to defeat these security holes, you need to understand exactly what they do.
1. The PHP "PHP2Shell" Exploits (CVE-2026-109618 & CVE-2026-109619)
The security community is calling this PHP2Shell. Disclosed by the Wiz Research Team, this attack is an incredibly dangerous "chain" of two separate critical errors deep inside the PHP core.
CVE-2026-109618 (Memory Management Error): Triggered when PHP runs out of memory while handling specific request processes.
CVE-2026-109619 (Use-After-Free Flaw): A memory corruption state where PHP's internal worker engine attempts to reuse data from memory that was already freed.
The Danger: An attacker can trigger these chained memory errors simply by sending a custom, malicious HTTP request to your site. They can execute any system command on your server (like shell_exec or download malware) without needing a password, account, or API key. Because it targets the PHP core, application firewalls and normal login protections in WordPress, Laravel, or Drupal can be bypassed.
2. The Node.js Brotli & TLS Exploit (CVE-2026-111497)
Node.js released synchronized emergency updates to patch 10 security bugs. The top-tier priority is a critical flaw within the heavily used Brotli compression engine.
CVE-2026-111497 (Brotli OOB Write): An out-of-bounds memory write error in Node's Brotli decompression handling.
The Danger: If your Node.js application accepts and de-compresses data payloads from clients, a bad actor can pass specialized compressed data to overflow the process memory, crash your app, or run malicious commands (RCE) on the host machine.
TLS Certificate Validation Bypass (CVE-2026-105483): Another high-severity bug that can bypass domain identity checks, paving the way for Man-in-the-Middle data sniffing.
🎯 Which Versions are Affected?
Check your setup against these specifics:
Technology | Vulnerable Versions | Safe/Patched Versions | Action Required |
PHP 8.5 |
|
| Upgrade runtime immediately |
PHP 8.4 |
|
| Upgrade runtime immediately |
PHP 8.3 |
|
| Upgrade runtime immediately |
PHP 8.2 |
|
| Upgrade runtime immediately |
PHP 8.1 & older | All sub-versions | None (End-of-Life) | Upgrade to a supported branch! |
Node.js 26 |
|
| Update Node.js package |
Node.js 24 |
|
| Update Node.js package |
Node.js 22 |
|
| Update Node.js package |
🛠️ Complete Guide: How to Fix (All Environments)
Simply restarting your tools or rebuilding code will not solve the issue. Use the appropriate guide below to ensure your setup fetches secure, patched base runtime packages.
Method A: Updating Containerized Apps (Docker & Docker Compose)
CRITICAL NOTE: Restarting a Docker container does absolutely nothing to fix this. To update container-level dependencies, you must download the fresh, secure version of the base image (like node:22 or php:8.3-fpm) from Docker Hub, completely bypassing Docker's speed-oriented caching system.
Here is how to force an update on any platform (Linux, macOS, or Windows CMD/PowerShell):
Step A1: Flush and Rebuild the Images
Open your terminal (Linux/macOS) or Command Prompt/PowerShell (Windows) in your project directory and run:
For Standard Docker CLI:
Bash
docker build --pull --no-cache -t your-app-name:latest .
(The --pull flag tells Docker to download the updated image from the registry. The --no-cache forces it to rebuild your app without utilizing vulnerable local memory.)
For Docker Compose Applications:
Bash
docker compose build --pull --no-cache
Step A2: Stop and Force-Recreate Your Running Containers
You must terminate the old application tasks and run the new code.
For Standard Docker CLI:
Bash
# 1. Stop the old, vulnerable container
docker stop your_active_container

# 2. Delete it so the namespace is free
docker rm your_active_container

# 3. Spin up the new one (using your actual launch options)
docker run -d --name your_active_container your-app-name:latest
For Docker Compose Applications:
Bash
docker compose up -d --force-recreate
Step A3: Verification Check
Confirm Docker is indeed using today's fresh build:
Bash
docker inspect -f '{{.Created}}' your-app-name:latest
(Verify the output timestamp. If the date and time correspond to today, your containerized setup is safe.)
Method B: On Local and Native Servers (Linux OS)
If you are running direct virtual machines or bare-metal instances on Ubuntu, Debian, or Red Hat:
For PHP (Debian/Ubuntu):
Bash
# 1. Pull update listings
sudo apt update

# 2. Run system upgrades specifically targeting PHP packages
sudo apt --only-upgrade install php8.5 php8.5-cli php8.5-fpm php8.5-common php8.5-opcache php8.5-xml php8.5-curl

# 3. Restart your web server daemon
sudo systemctl restart php8.5-fpm
sudo systemctl restart nginx # Or 'apache2'
(Swap out 8.5 with your active minor version, such as 8.4, 8.3, or 8.2.)
For Node.js via NVM (Node Version Manager) — Best for all Platforms:
Using NVM is the easiest, most seamless way to avoid system errors on Windows, macOS, and Linux:
Bash
# 1. Grab the latest patched version
nvm install 22 --reinstall-packages-from=current

# 2. Configure nvm to utilize the updated installation
nvm use 22

# 3. Apply it system-wide
nvm alias default 22

# 4. Double check it worked
node -v
(Adjust 22 to 24 or 26 depending on your active Node runtime.)
Method C: On Local Windows (WSL & Native PowerShell)
Fix WSL (Windows Subsystem for Linux)
Open your WSL terminal and update dependencies by running:
Bash
sudo apt update && sudo apt install --only-upgrade php8.3-fpm nodejs
Fix Local Native Windows (Using Chocolatey)
If you rely on the Windows package manager "Chocolatey" to handle your native stack:
PowerShell
# In PowerShell (Run as Administrator)
choco upgrade php -y
choco upgrade nodejs -y
Manual Updates (Without Tools)
For PHP: Go to the official PHP Windows binaries page (
windows.php.net), download the.zipupdate, and extract it to your current PHP install directory (oftenC:\php). Make sure to overwrite older files and restart IIS or Apache.For Node.js: Download the safe
.msisetup file directly fromnodejs.organd go through the steps. It will overwrite the insecure, outdated Node executables automatically.
🔒 Post-Patch Checklist
Before wrapping up your updates, perform these essential safety checks:
Stop Legacy Fallback: Verify your local PHP processes do not allow automatic CGI fallbacks. In your
php.ini, ensurecgi.fix_pathinfo=0is active to prevent other related directory parsing flaws.Review Package Upgrades: If your app is live, test all internal functions. An out-of-bounds update could alter system behaviour (though security hotfixes rarely cause issues).
Deploy Protection: Place critical infrastructure behind robust Firewalls (Cloudflare, AWS WAF, or digital load-balancers) to detect and block RCE attempts aimed at unpatched modules.
Take 15 minutes to secure your stack today. A little preventive maintenance can prevent a significant security incident later! Use the links below to check your servers, verify image builds, and make sure your applications are fully patched. Let’s keep rifatxtra.com and the wider web secure.
Frequently asked
Are older PHP versions like 7.4 or 8.1 getting a patch for PHP2Shell?
No. Official patches were only released for supported branches (8.2 through 8.5). While minimal source backports exist for 7.4 to 8.1, you will need to manually compile them or rely on third-party OS vendor patches. The best solution is upgrading your stack to PHP 8.2+.
Can my application-level authentication block the PHP2Shell exploit?
No. Researchers confirmed that PHP processes the malicious payload and executes the code before any of your application routing or authentication logic runs.
What Node.js versions are affected by the Brotli RCE flaw?
CVE-2026-111497 affects all three active Node.js release lines: 22.x, 24.x, and 26.x. You must update to 26.12.1, 24.22.1, or 22.23.4.